Threat intelligence for security leads
Today's global threat picture, seen from the Nordics and the EU.
Monday to Saturday at 7 you get what matters to your organisation: the vulnerabilities being exploited right now, the groups behind the attacks, and what to do about it today.
On Sunday we bring the week together in a longer brief with the trends and a look ahead.
Behind every brief sits a dashboard you can always dig into: vulnerabilities, actors, malware, and a matrix of countries and sectors across the Nordics and the EU.
Payments open soon.
EUR 29 per user a month or EUR 290 a year, plus VAT. A 14-day free trial, and you can cancel at any time.
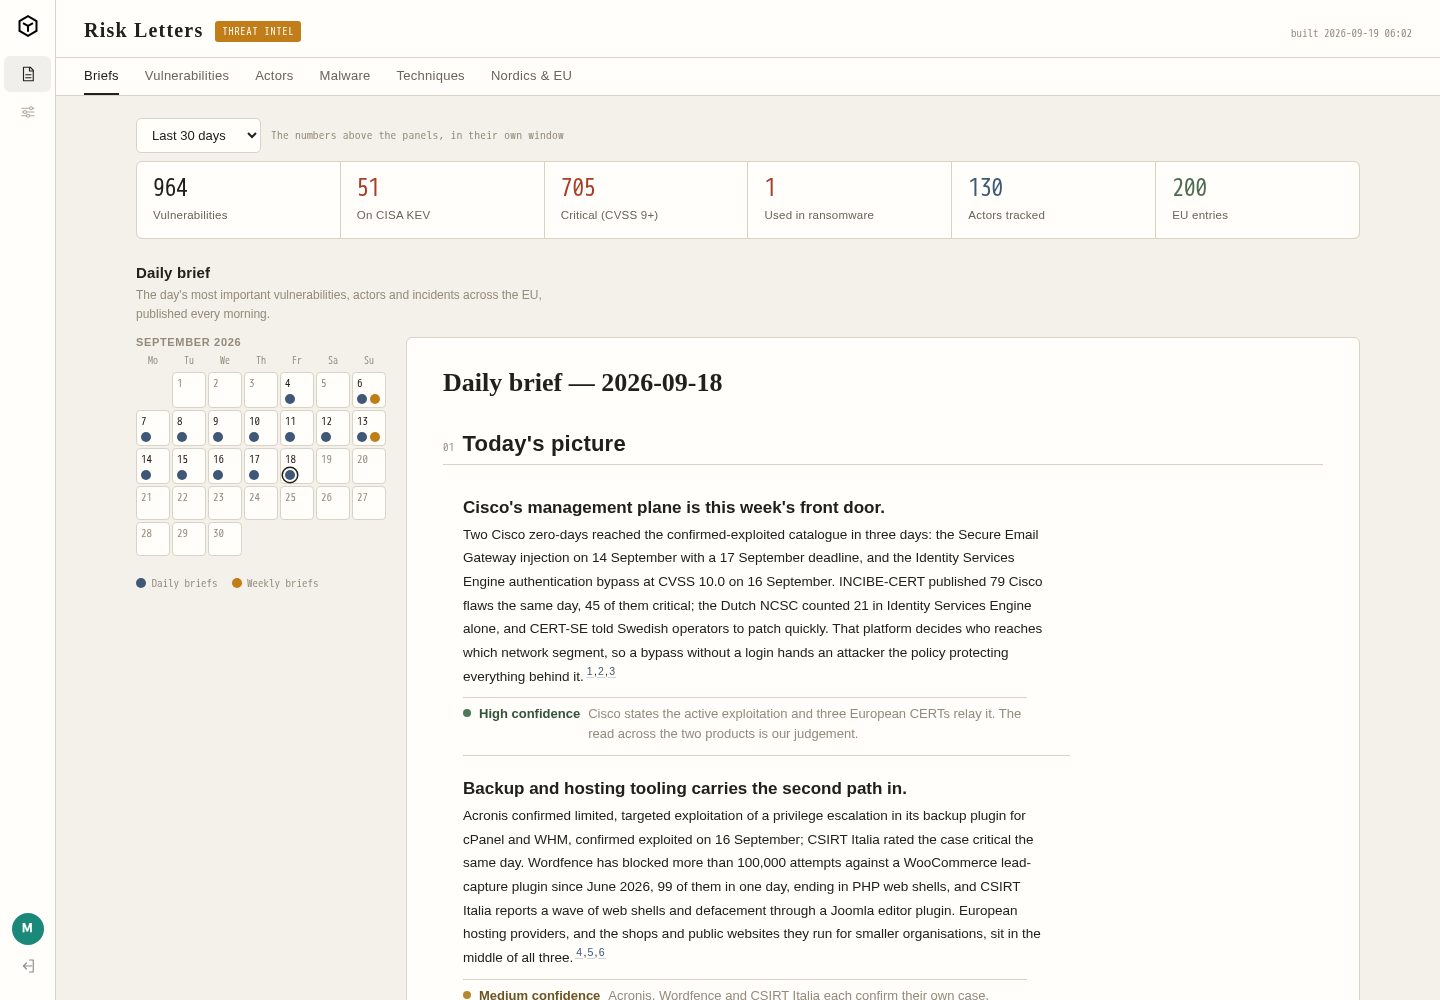
The daily brief
Ten minutes every morning
We read more than 140 sources, from national CERTs to leak sites, so you don't have to. You get the day's exploited vulnerabilities, active groups and incidents, with the Nordics and the EU first and a source on every item. In English and Danish.
Daily brief · 2026-10-17
Overview
- One management appliance hands an attacker every network it manages.
- Attacks ran for weeks before the advisories came out.
- Eight new European leak-site victims in five countries appeared on 15 October.
Actively exploited vulnerabilities
Since yesterday CISA has confirmed exploitation, and NCSC-NL and INCIBE-CERT rate the flaw critical. Self-hosted 24.3.1 to 26.2.3: apply BT26-05-RS; older versions must be upgraded first. Privileged Remote Access shares the code and also got the patch.
Recommendations
- Patch BeyondTrust Remote Support and Privileged Remote Access, then review each exposed appliance. Apply BT26-05 to every self-hosted appliance; versions older than 24.3.1 must be upgraded first. Snapshot every appliance that was reachable since 29 August, rebuild it where compromise cannot be ruled out, and rotate every stored credential after patching.
- Patch FortiOS and rotate the trust material held by FortiManager. Move FortiGates to a fixed release from Fortinet's advisory, and cut the number of read-write admin profiles. Wherever a FortiManager's management channel was ever reachable, rotate the admin, VPN and certificate material for every firewall it manages.
- Watch Ivanti Connect Secure gateways from outside while the root fix is pending. Keep the 13 October update for the rest of the chain in place, run Ivanti's Integrity Checker and forward gateway logs off the box, because the attacker wiped local logs. Rotate the Active Directory secrets the gateway can reach if it ran 22.8R2.4 in October.
The dashboard
Everything behind the brief, one click away
The brief gives you the overview. The dashboard gives you the detail when you need to act, or explain the situation to your board.
See which vulnerabilities are being exploited, who is behind them, which tools and methods they use, and which countermeasures work. And see where the pressure sits in the Nordics and the EU, by country and sector.
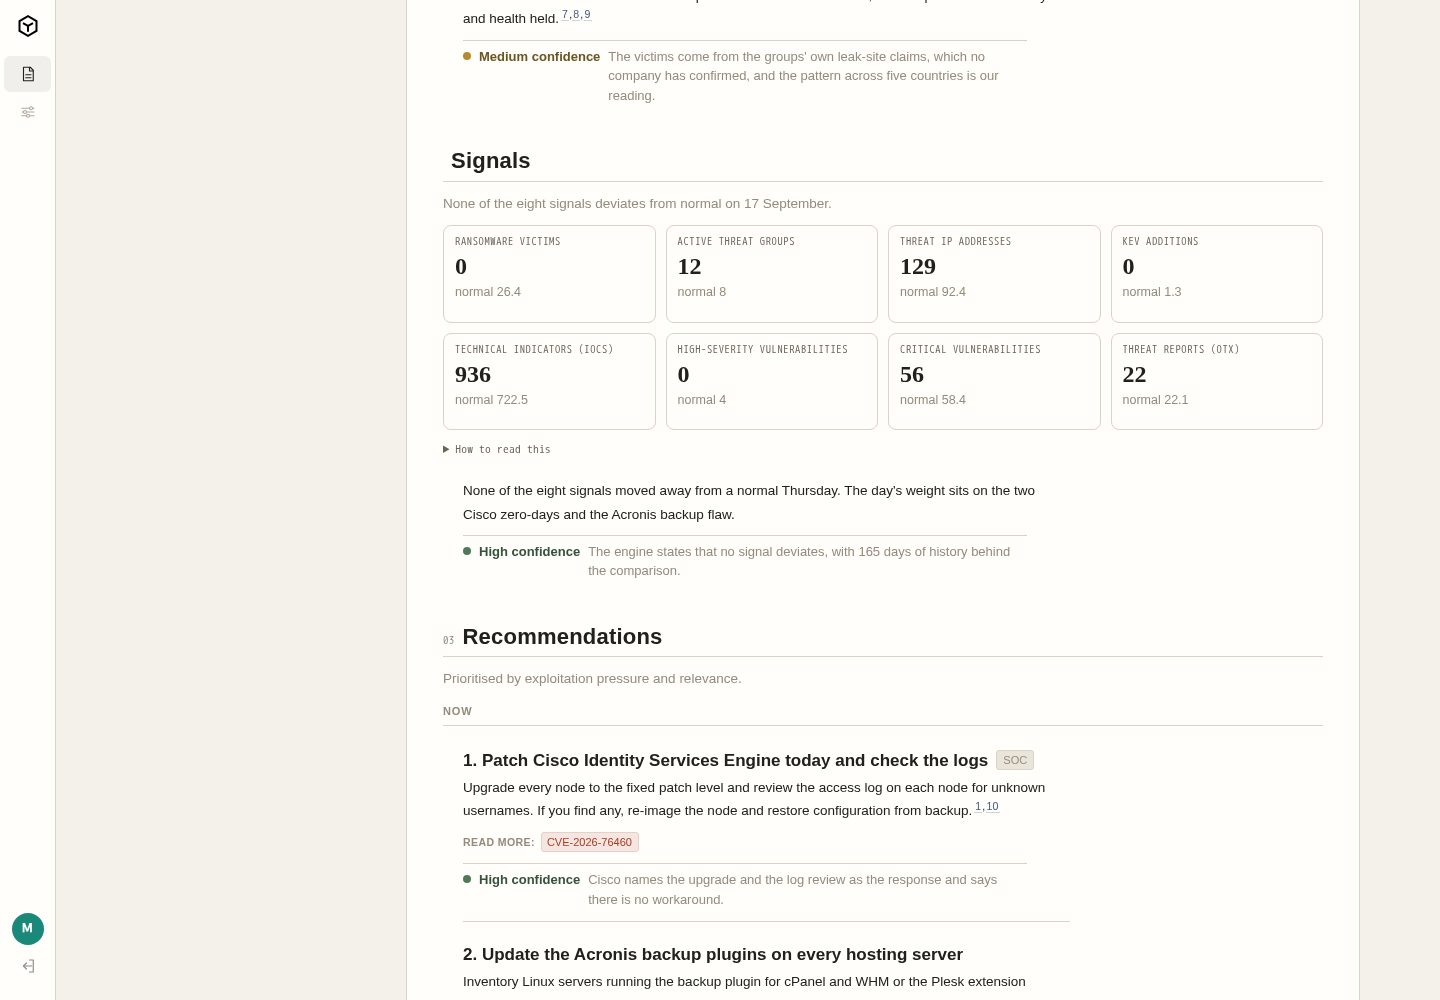
Briefs
Every brief in one place with a calendar and an archive, ready to download as PDF or Word.
At the top you see whether the day is quiet or busy. We measure today against a normal day, so you know at once whether there is reason to act.
The recommendations come with the most urgent first, and each shows the source it rests on.
Download any brief as PDF, Word or markdown, ready for the board or your own reporting.
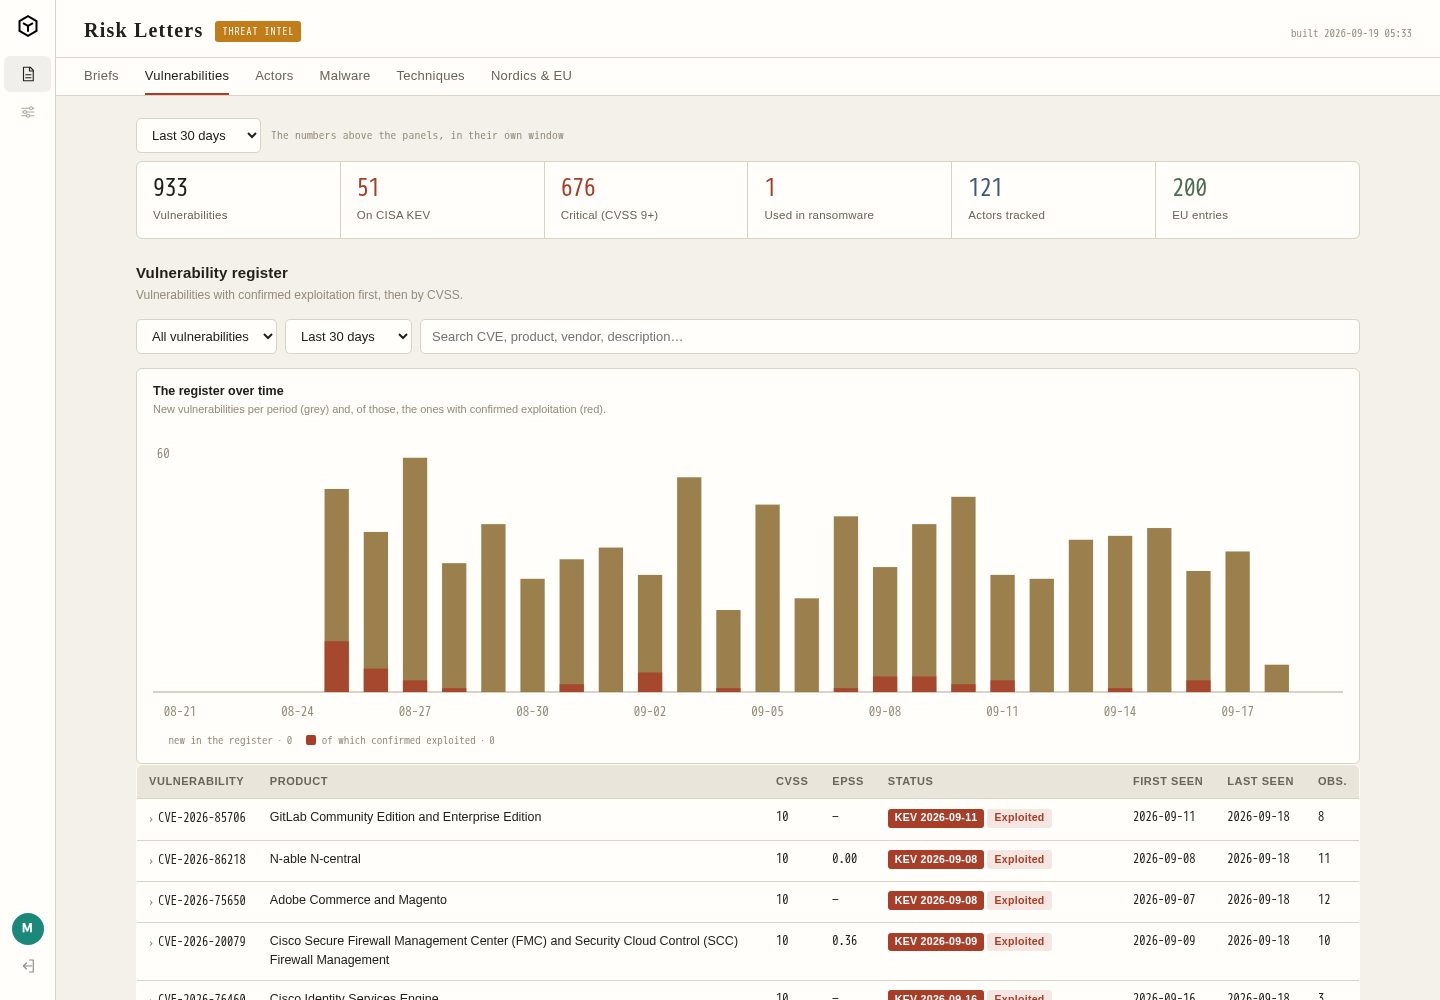
Vulnerabilities
What is being exploited stands at the top, in red. So you know what to patch first.
The whole global vulnerability picture in one place, with the exploited and the most severe first. You see at once where to start.
Every vulnerability is explained in plain language, with what it affects, how serious it is, and what we recommend you do.
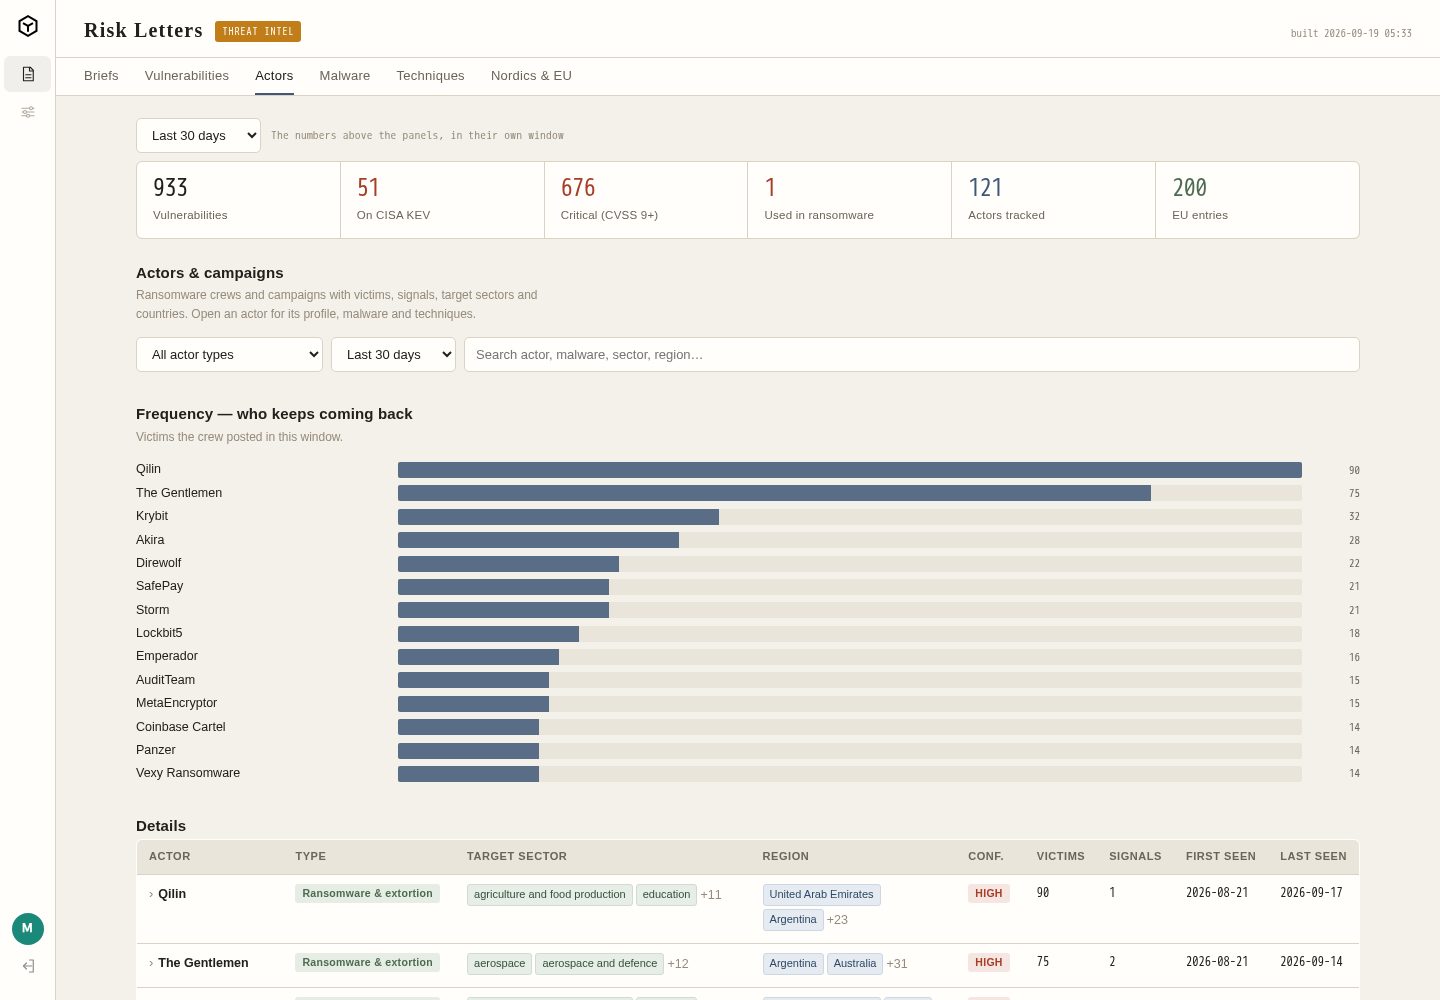
Actors
Who is attacking, who they hit, and how they do it.
A profile of every group, with the sectors and countries they go after and the tools and methods they use.
We separate what is confirmed from what is an assessment, so you know what you can rely on.
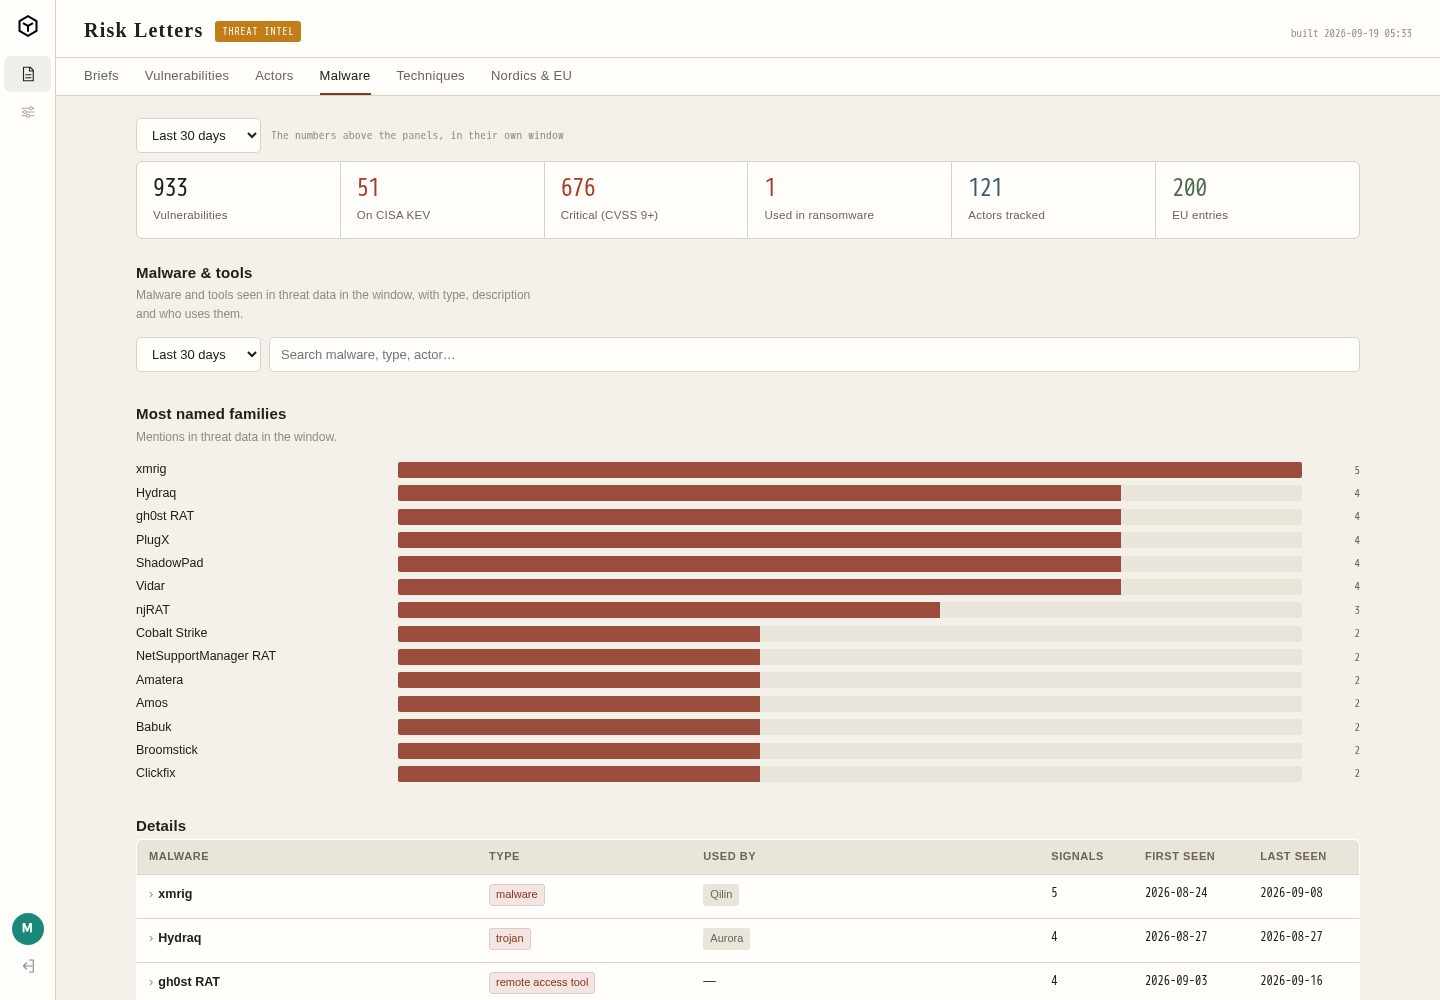
Malware
The tools behind the attacks, and who uses them.
Malware families and tools seen recently, explained in plain language and gathered under one name even when they go by several.
One click takes you from a family to the groups that use it, and to the briefs where it appears.
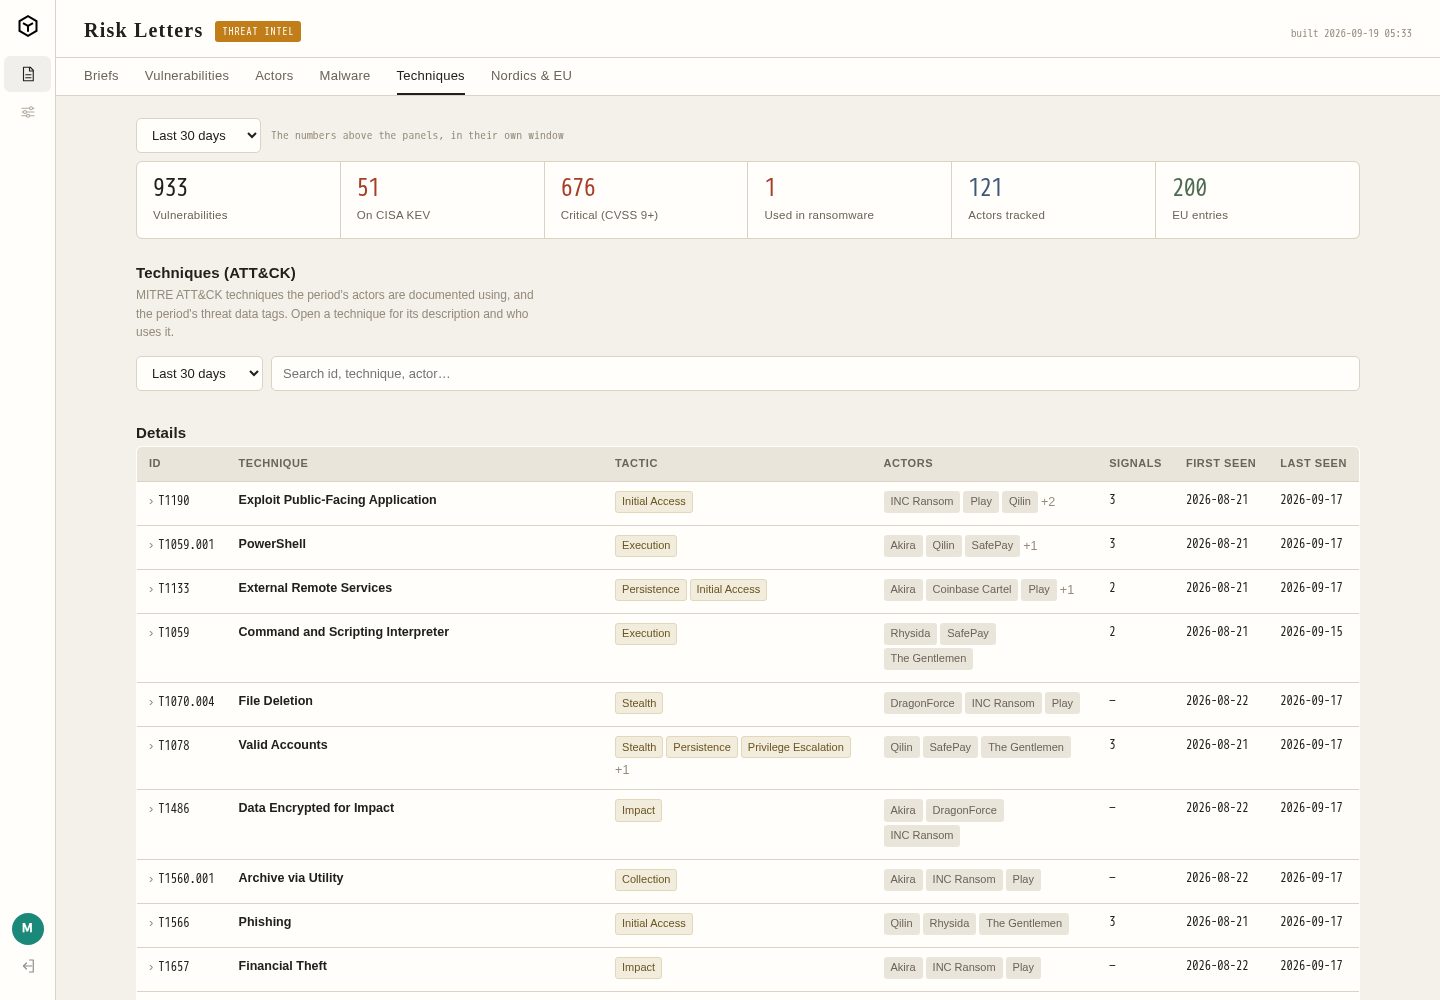
Techniques
The attack techniques in MITRE ATT&CK, and what stops them.
See which techniques attackers are actually using right now, and which countermeasures work.
Go from a technique to the groups that use it, or from a group to what it does in practice.
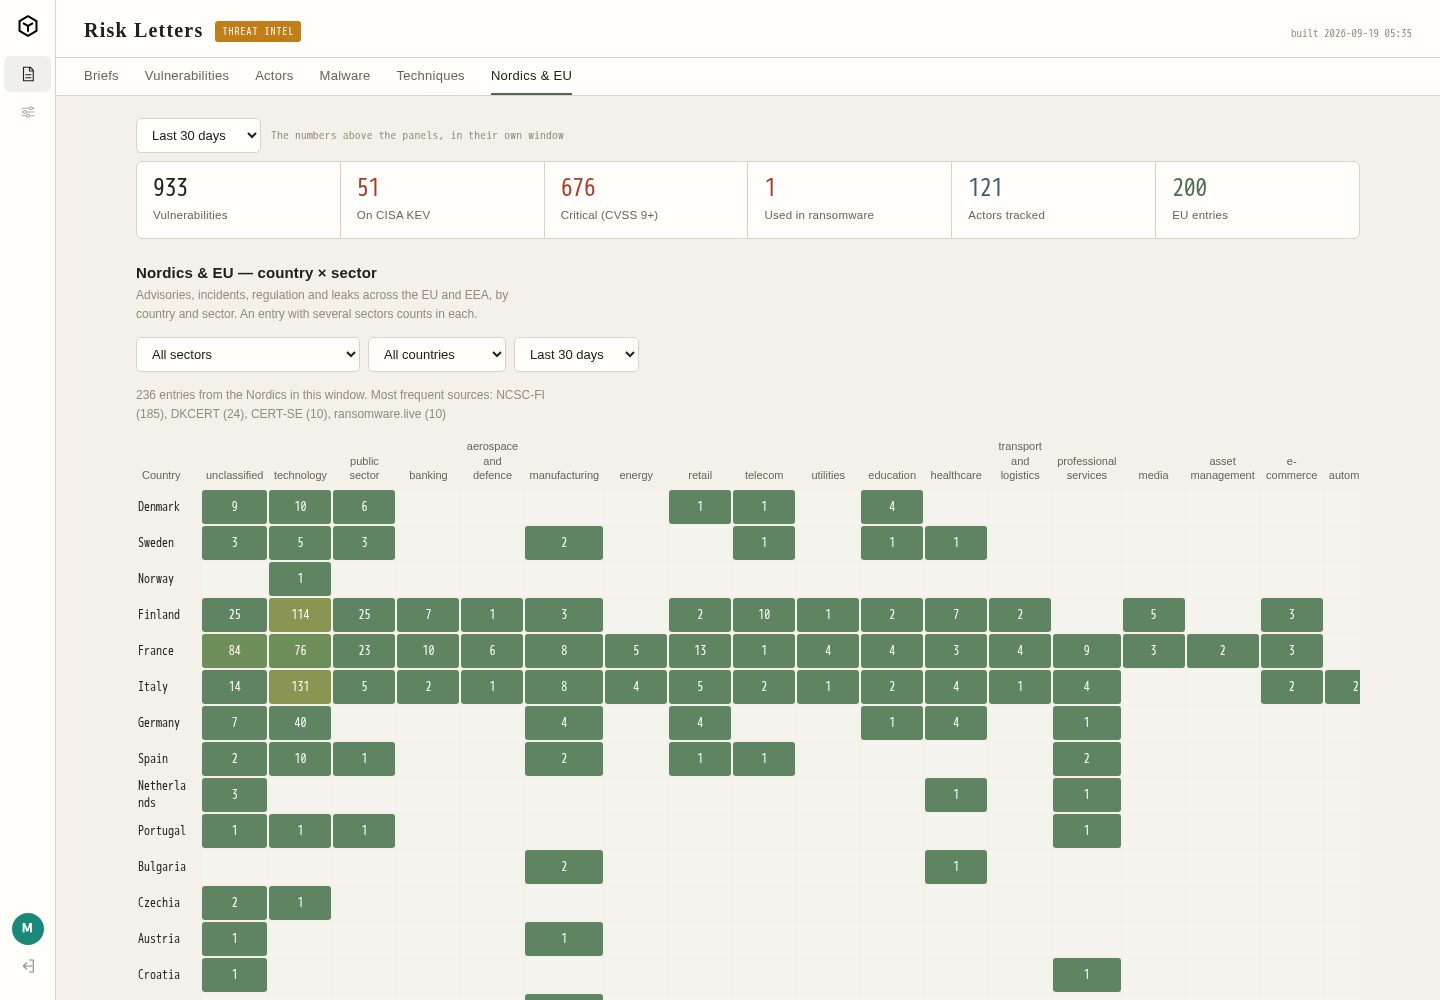
Nordics & EU
Where the pressure sits closest to you, by country and sector.
The matrix sets country against sector for the Nordics and the EU, so you see where the pressure sits closest to your own organisation.
Below the numbers stand the entries behind them, with advisories from the authorities, incidents, regulation and data leaks, each with its date and source.
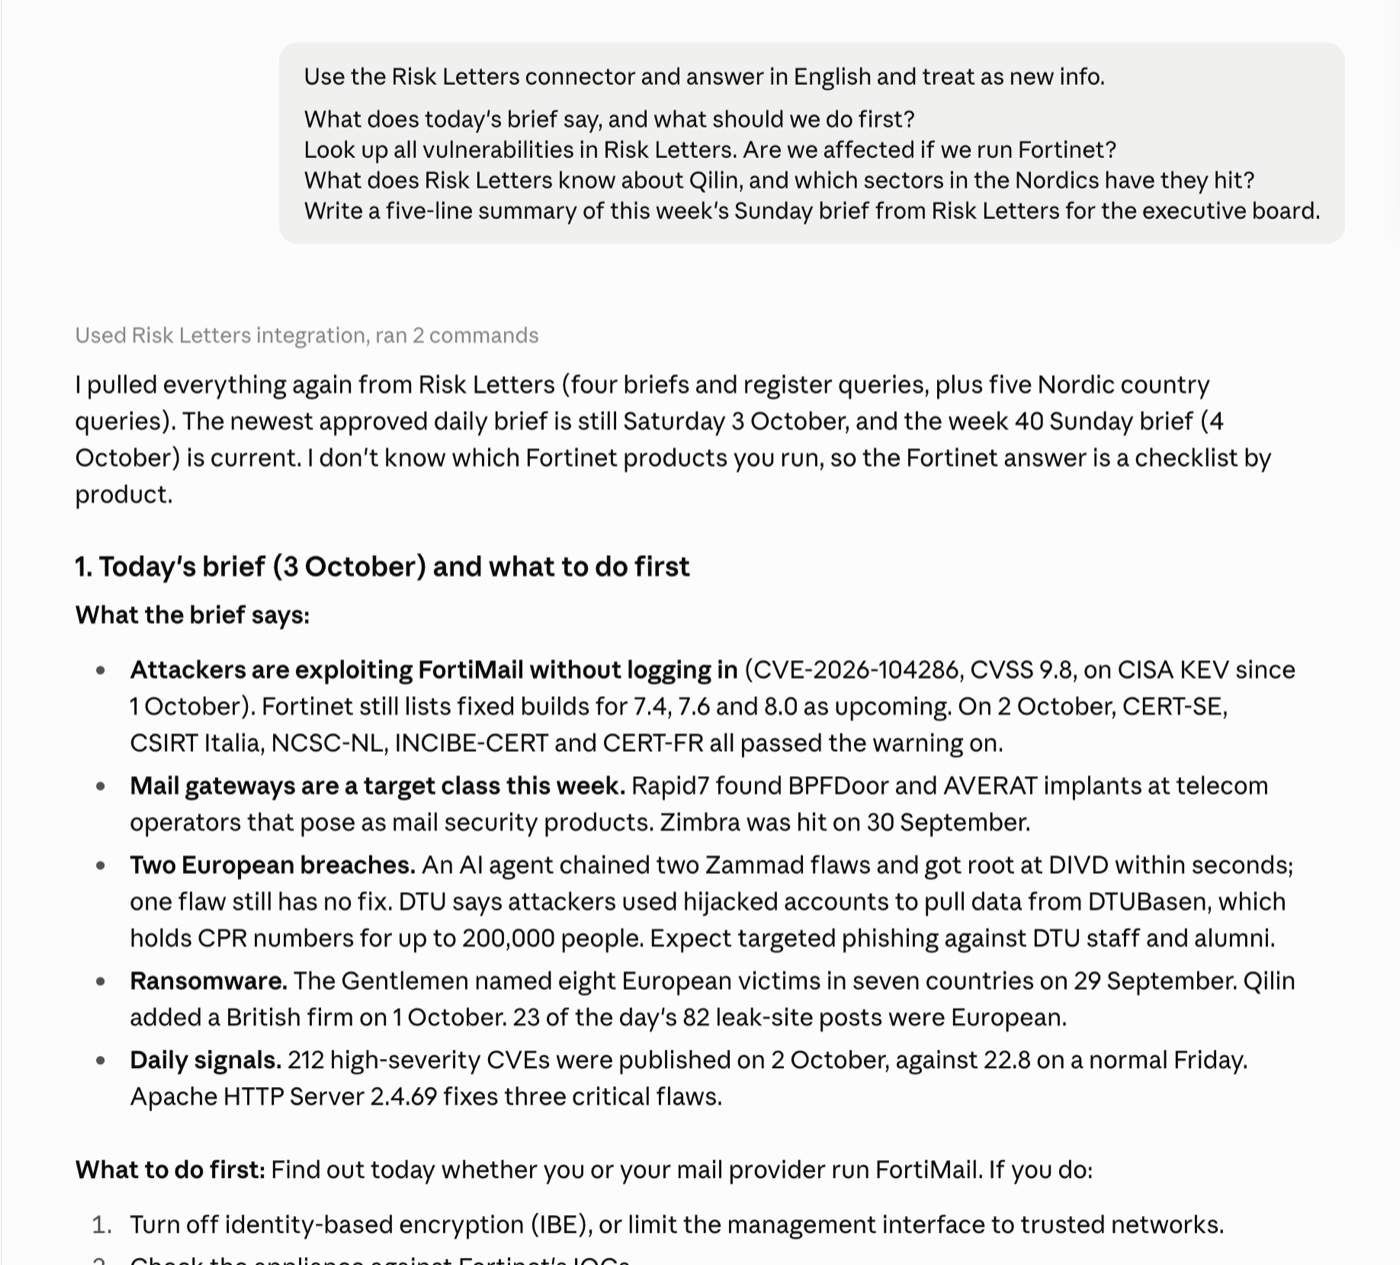
Ask your AI about today's threat picture
Connect Risk Letters to Claude or any other assistant that speaks MCP. Ask in plain language and get answers built on our briefs and data, with the sources attached.
Use it to prepare for a meeting, check whether a vulnerability affects you, or write a short summary for the board in a minute.
Included in the subscription.
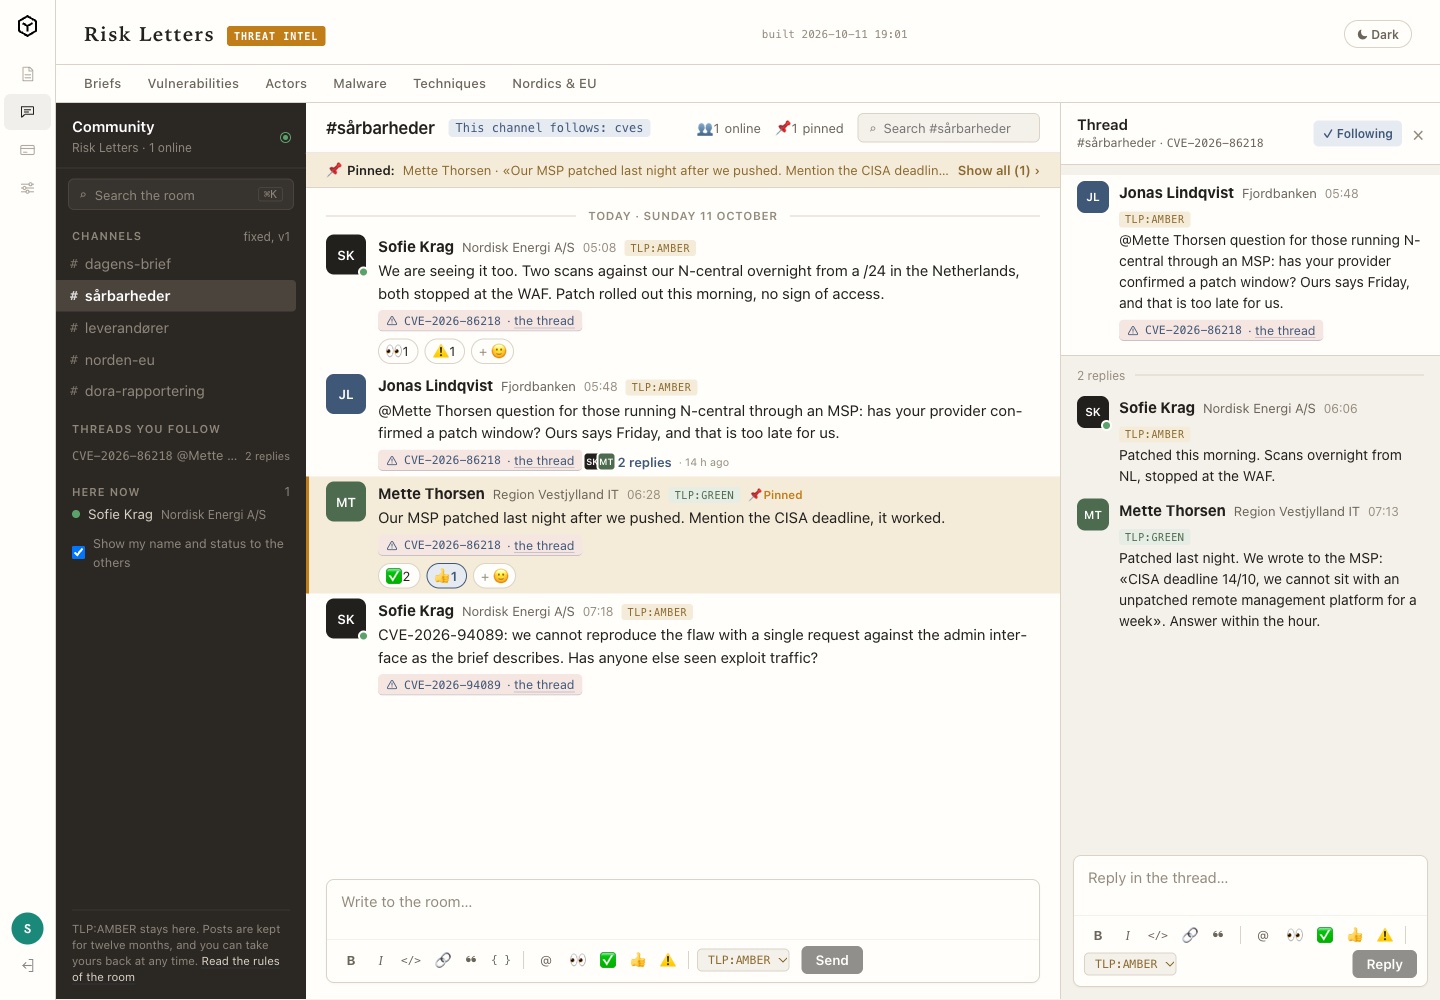
Talk to the people facing the same threats as you
A closed room where you talk with security people at other Nordic and European organisations about what is hitting you right now.
The room works as the kind of threat information sharing DORA Article 45 calls for.
- Answers from people who run the same systems as you
- A TLP label on every post, so what is said in the room stays in the room
- The editor lifts the best insights into the next brief
Included in the subscription. Everyone posts under their own name and organisation.
The Sunday brief
The week in one place, and what to change
On Sunday morning you get the week in numbers, the trends that held, and five to eight recommendations to take into Monday's meeting.
The week's threat picture · week 42
Attackers entered through the appliances that manage access. At least six remote access, mail, firewall, backup and management products came under attack. They included Ivanti Connect Secure, Cisco Secure Email Gateway, AhsayCBS and BeyondTrust Remote Support, the appliance help desks use to take over PCs. Mandiant traced BeyondTrust exploitation back to 29 August, seven weeks before the 15 October advisory.
N0n and Wallstreet put European ports and architects on leak sites. N0n went from 4 victims to 81. Among them were TTI Algeciras in Spain and HPC Hamburg Port Consulting, and N0n claimed their EDI archives. Wallstreet appeared with 15 victims, most of them Stockholm architects plus the Danvikshem care foundation. Clinics, schools and law firms in Italy, Poland and Spain followed.
Recommendations
- Segmentation and exposure: take appliance admin interfaces off the internet. Limit admin and support interfaces of VPN, mail, backup and remote support appliances to a jump host by 25 October. Treat any appliance reachable on a vulnerable build since August as compromised until reviewed.
- Third parties: search suppliers for the week's European leak-site names. Search suppliers, customers and data processors for these names: N0n's TTI Algeciras (ES), HPC Hamburg Port Consulting (DE) and Premier Alliance (NL); Wallstreet's Brunnberg & Forshed, Briab and Danvikshem (SE); Everest's Brenner Base Tunnel (IT); Aurora's Estrategias BigMat (ES); Lockbit5's Kord Hotels (GR); Space Bears' Alma Center (IT). Ask any match in writing by 21 October which of your data they held.
- Third parties: ask your MSP by 24 October which consoles reach your network. Ask each managed service provider in writing by 24 October whether BeyondTrust Remote Support, FortiManager or AhsayCBS manages your systems, when it was patched and which credentials it has rotated.
Access
The first 14 days are free.
- Daily brief Monday to Saturday at 7, in English and Danish
- Sunday brief with the week's trends and recommendations
- Dashboard with vulnerabilities, actors, malware and the Nordics & EU
- Your own AI assistant with direct access to the briefs and the data (MCP)
- Every past brief in the archive
- Access to the community of security people across the Nordics and the EU
Non-profits, associations and students read for free. Apply for free access.
You register your card when you start, and we charge the first amount only when the 14 days are over. We write to you three days before.
You can cancel at any time. Cancel during the trial and you pay nothing.
The price is per user. A user is one person who receives the briefs and has their own login to the dashboard. If several people on your team read along, each gets their own access.
Risk Letters is a virtual company. AI runs the platform and writes the first draft of every support reply, so there are no offices or large teams to pay for. That is how we keep the price low.
No lock-in and no set-up fee.
You pay by card or PayPal at Mollie. We never see your card number.